Fact sheet · Security, Privacy & Compliance

Penetrify
Cloud-based AI penetration testing platform that automatically scans web applications and APIs for OWASP Top 10 vulnerabilities and delivers audit-ready reports in minutes.
Penetrify specifications
| Section | Security, Privacy & Compliance |
|---|---|
| Founded | 2024 |
| Origin | Brno, Czech Republic |
| Stage | Startup |
| Website | penetrify.cloud |
| Makers | Viktor Bulanek (Founder) |
| Votes2 | 0 |
Penetrify metrics
| Metric | Value |
|---|---|
| Domain Rating | 36 +1 (up) since last check |
| Trust Flow | 24 no change since last check |
| Citation Flow | 32 no change since last check |
| Referring domains | 168 no change since last check |
| External backlinks | 374 no change since last check |
Fact: Ahrefs Domain Rating checked 16 Oct 2026, fact changed 11 Oct 2026. Fact: top topic Computers/Security (24). Fact: Majestic checked 5 Oct 2026, fact changed 5 Oct 2026. Link facts from Majestic. Trust Flow, Citation Flow and Topical Trust Flow are trademarks of Majestic-12 Ltd.
Penetrify domain fact sheet
| Domain age | 8 months |
|---|---|
| Registered | |
| Expires | |
| Registrar | Amazon Registrar, Inc. |
| DNSSEC | Not signed |
Cloud-based AI penetration testing platform that automatically scans web applications and APIs for OWASP Top 10 vulnerabilities and delivers audit-ready reports in minutes.
Overview
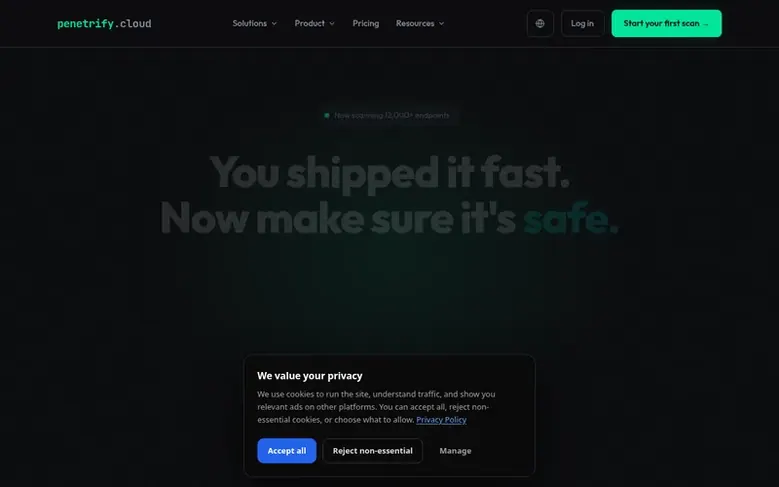
Penetrify is an autonomous AI penetration testing platform built for teams without dedicated security staff. The platform automatically scans web applications and APIs for vulnerabilities across all OWASP Top 10 categories, testing authentication flows, access control, injection attacks, API security, and business logic flaws. It maps attack surfaces, chains findings together like a human pentester would, and delivers actionable reports with severity ratings and fix guidance in minutes instead of weeks.
Unlike traditional manual penetration testing that costs $15,000-$50,000 and happens once annually, Penetrify runs on every deployment through CI/CD integration or on demand. The AI agent performs read-only testing without modifying data, maintains a false positive rate below 5%, and operates entirely within EU jurisdiction under GDPR. No installation, agents, or infrastructure changes are required—users simply add their application URL and receive results in under 30 minutes.
The platform is designed specifically for startups, indie builders, SaaS companies, fintech platforms, and healthcare applications that need continuous security testing at a price point accessible to teams without large security budgets.
Feature facts
- Automated OWASP Top 10 vulnerability scanning
- AI-driven attack surface mapping
- IDOR and broken access control detection
- Multi-step attack chain simulation
- GraphQL and REST API security testing
- CI/CD pipeline integration
- Unlimited retesting after fixes
- Read-only non-destructive scanning
- Results in under 30 minutes
Pricing
Pricing model: Paid
From $100 per month with unlimited retests included
Compare and explore
Frequently looked up
- Q1What is Penetrify?
- Penetrify is an autonomous AI penetration testing platform that automatically scans web applications for security vulnerabilities, simulating real-world attacks to identify weaknesses such as SQL injection, XSS, CSRF, IDOR, and hundreds of other vulnerability classes.
- Q2How does AI penetration testing work?
- The AI agent autonomously explores a web application, maps its attack surface, and executes a wide range of security tests from input validation and authentication bypass to privilege escalation and business logic flaws, operating like a skilled human tester but running continuously at machine speed.
- Q3Is Penetrify a replacement for manual penetration testing?
- Penetrify complements manual pentesting by providing continuous, automated coverage between engagements, catching the majority of common vulnerabilities automatically. For complex business-logic vulnerabilities or compliance-mandated assessments, a human pentest may still be recommended.
- Q4What types of vulnerabilities does Penetrify detect?
- Penetrify detects all OWASP Top 10 categories including SQL injection, Cross-Site Scripting (XSS), Cross-Site Request Forgery (CSRF), Insecure Direct Object References (IDOR), broken authentication, security misconfigurations, sensitive data exposure, XXE injection, broken access control, and many more.
- Q5Is it safe to run penetration tests on production?
- Yes. Penetrify is designed to be safe for production environments. Our AI agent avoids destructive operations and focuses on detection rather than exploitation. That said, we recommend testing on a staging environment first, or scheduling scans during low-traffic periods as a precaution.
Find Penetrify online
Leave a review for Penetrify
Review count for Penetrify: none yet. Add the first.
Fact: reviews are free and cannot be bought. All reviews, in brief
Reviews and facts · Fact updates · Share these facts · Your SaaS? Claim this fact file · Report a wrong fact
Penetrify has a free listing. The owner can unlock the full profile with a paid launch for $5:
- Founder story (locked)
- Milestones (locked)
- Demo video (locked)
- Dofollow website link (locked)
See also
| Product | Origin | DR1 | Votes2 |
|---|---|---|---|
 PortreeveStop trial abuse, AI credit farming and referral fraud | not stated | 4 | 0 votes. Log in to vote for Portreeve in the file |
 ArkWardenEncrypted photo and file vault for iPhone with pattern unlock and no account required | not stated | 28 | 0 votes. Log in to vote for ArkWarden in the file |
 SealbyPrivate encrypted vault for iPhone and iPad with hidden vaults and no backdoor | Czech Republic | 33 | 0 votes. Log in to vote for Sealby in the file |
 TabToCartAutomated accessibility monitoring for e-commerce checkouts | France | 0 | 0 votes. Log in to vote for TabToCart in the file |