Fact sheet · Cybersecurity
Pharon
Security incident alerts for your whole stack
A warning system that keeps an inventory of packages, container images, GitHub Actions, runtimes and cloud services, and alerts teams within minutes when
Overview
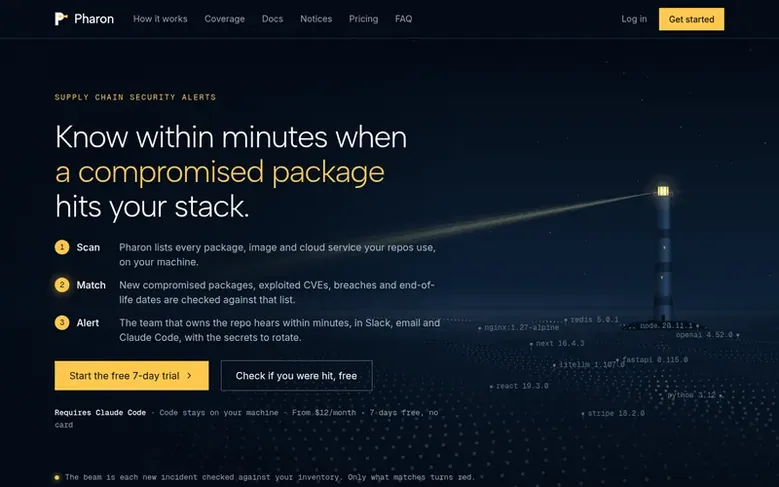
Pharon monitors software stacks across multiple layers including npm and PyPI packages, container images, GitHub Actions, Node.js and Python runtimes, cloud services like Postgres and Redis, Kubernetes, Lambda, and third-party services including Stripe, OpenAI, Vercel and Supabase.
The product scans components on your machine and uploads only an inventory of names, versions and file paths—source code and file contents never leave your machine. It checks this inventory against incident sources including OSV.dev, GitHub Advisory Database, CISA's catalog of exploited vulnerabilities, endoflife.date, and security news, checking for new compromises every 5 minutes.
Alerts reach teams through Claude Code, email, Slack and webhooks. Critical and high severity incidents go out immediately while others arrive in a daily digest. The tool includes a local check command that shows which components on a specific machine are affected and names secrets that need rotation.
Pharon integrates with GitHub Actions to fail pull requests that introduce components with open incidents and displays warning indicators in Claude Code when teams are working in affected repositories.
Feature facts
- Inventory of packages, container images, GitHub Actions, runtimes and cloud services
- Real-time incident alerts across OSV.dev, GitHub Advisory, CISA KEV and security news
- Local machine checks without reading source code or secrets
- GitHub Action for pull request checks and inventory updates
- Support for 50+ third-party services including Stripe, OpenAI, Vercel and Supabase
- Signed notices with Ed25519 to verify authenticity
Pricing
Pricing model: Freemium
Solo $12/month for up to 10 projects with 1 member; Team $49/month for up to 25 projects with unlimited members; Business $199/month for up to 150 projects with unlimited members and priority support. Free 7-day trial with no card required.
Follow Pharon: their milestones, new launches and awards come to you by email, once a day by default.
Pharon specifications
| Section | Cybersecurity |
|---|---|
| Origin | London, United Kingdom |
| Stage | Startup |
| Website | getpharon.com |
| Votes2 | 0 |
Pharon metrics
| Metric | Value |
|---|---|
| Domain Rating | 0 no change since last check |
| Trust Flow | 2 no change since last check |
| Citation Flow | 17 no change since last check |
| Referring domains | 7 no change since last check |
| External backlinks | 39 no change since last check |
Fact: Ahrefs Domain Rating checked 16 Nov 2026, fact changed 16 Nov 2026. Fact: top topic Computers/Internet/Web Design and Development (2). Fact: Majestic checked 16 Nov 2026, fact changed 16 Nov 2026. Link facts from Majestic. Trust Flow, Citation Flow and Topical Trust Flow are trademarks of Majestic-12 Ltd.
Pharon domain fact sheet
Open the fact sheet
| Domain age | 23 days |
|---|---|
| Registered | |
| Expires | |
| Registrar | NameCheap, Inc. |
| DNSSEC | Not signed |
Pharon launch receipt sheet
What we have measured for Pharon since it went live on SaaS Directory Info on 16 November 2026.
- 0 Domain Rating (Ahrefs)
first measured 16 Nov 2026 - 2 Trust Flow (Majestic)
first measured 16 Nov 2026 - 7 Referring domains (Majestic)
first measured 16 Nov 2026
Day 0 since launch. Next receipt: day 30, 16 Dec 2026. The figures report a change; they do not say what caused it, and many things can. No figure here is a guess.
Got a launch coming up?
Step-by-step tips for before, during and after your launch, free to read on SaaS Directory Info.
- Prepare
- Launch day
- Launch week
- Next steps
Compare and explore
Frequently looked up
- Q1What is Pharon?
- Pharon is a warning system for software teams that keeps an inventory of every package, container image, GitHub Action, runtime and cloud service you run, and alerts you within minutes when a compromised release, an exploited vulnerability, a vendor breach or an end-of-life deadline reaches it.
- Q2Does Pharon see my source code?
- No. The scan runs on your machine and uploads only an inventory: component names, versions and the paths of stack files. Source code, file contents and secret values never leave your machine, and the /pharon:show command prints the exact upload.
- Q3How quickly will I hear about a compromised package?
- Pharon checks OSV.dev and security news every 5 minutes, and CISA KEV and end-of-life dates daily. When a notice affects something you run, critical and high alerts go out right away and the rest arrive in a daily digest, unless you choose otherwise.
- Q4Does it replace my dependency scanner?
- No. A dependency scanner keeps your packages patched. Pharon tells you when something you already run has been compromised, exploited or retired, across the whole stack, and whether you were exposed.
- Q5What counts as a project?
- A repository linked with /pharon:setup. Branches, previews and your public DNS footprint do not count.
Leave a review for Pharon
Review count for Pharon: none yet. Add the first.
Fact: reviews are free and cannot be bought. All reviews, in brief
Reviews and facts · Fact updates · Share these facts · Your SaaS? Claim this fact file · Report a wrong fact
Pharon has a free listing. The owner can unlock the full profile with a paid launch for $5:
- Founder story (locked)
- Milestones (locked)
- Demo video (locked)
- Dofollow website link (locked)
See also
| Product | Origin | DR1 | Votes2 |
|---|---|---|---|
 VulnCueWordPress vulnerability detection and prioritization from public information | Spain | 1 | 0 votes. Log in to vote for VulnCue in the file |
| InvarSec, Inc.Deterministic runtime execution gateway and AI agent security for autonomous systems and microservices | United States | 0 | 0 votes. Log in to vote for InvarSec, Inc. in the file |
 T4X ProtectionDefense at the Atom | Bangladesh | 0 | 0 votes. Log in to vote for T4X Protection in the file |
 VeilleStop bots and account abuse in minutes | France | 27 | 0 votes. Log in to vote for Veille in the file |