Fact sheet · Security, Privacy & Compliance
SAML Chaos Lab
Enterprise SAML 2.0 fault-injection and SSO switchboard for negative testing
Automate SAML 2.0 negative testing to prevent certificate rotation outages, XML signature wrapping exploits, and pass enterprise SSO security reviews.
Overview
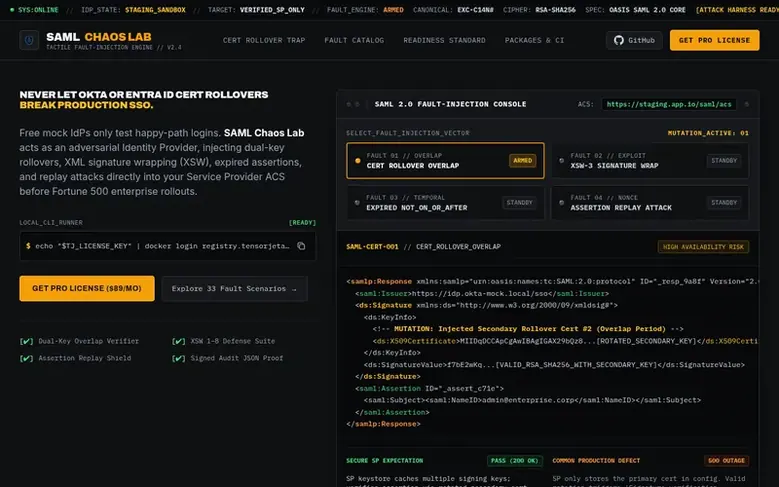
SAML Chaos Lab is an adversarial Identity Provider that injects fault scenarios directly into Service Provider testing environments. It automates SAML 2.0 negative testing with 33 CVE scenarios covering dual-key rollovers, XML signature wrapping (XSW), expired assertions, and replay attacks—issues that mock IdPs with static certificates cannot detect.
The platform generates signed audit proof artifacts to help pass enterprise vendor reviews from Fortune 500 banks, healthcare networks, and defense contractors. It supports both local CLI testing with 6 baseline checks and continuous CI/CD deployment with full scenario coverage.
Key capabilities include dual-key overlap verification, XSW 1–8 defense suite, assertion replay shield, and machine-readable JSON attestation signed for SOC 2 and ISO 27001 compliance. The service guarantees zero production SSO lockouts during Okta and Entra ID certificate rotation periods.
Feature facts
- 18 fault injection scenarios covering key lifecycle, trust boundaries, XML integrity, temporal validity, and replay defense
- Dual-key overlap verification for certificate rollovers
- XSW 1–8 defense suite for XML signature wrapping exploits
- Assertion replay shield with Redis TTL cache
- Signed audit JSON proof for SOC 2 and ISO 27001 compliance
- Local CLI and Docker runner for workstation testing
- CI/CD integration for GitHub Actions and CI pipelines
- SARIF, JSON, and HTML report generation
- Enterprise readiness index and cryptographic attestation
Pricing
Pricing model: Freemium
Community CLI Lab: Free (6 baseline checks, local CLI and Docker runner). 14-Day Release Pass: $179 one-time (all 33 CVE scenarios, single target host). Pro CI/CD License: $89/month or $790/year (unlimited CI runs, up to 2 target hosts, all 33 scenarios).
Follow SAML Chaos Lab: their milestones, new launches and awards come to you by email, once a day by default.
SAML Chaos Lab specifications
| Section | Security, Privacy & Compliance |
|---|---|
| Stage | Startup |
| Website | saml.tensorjetai.com |
| Votes2 | 0 |
SAML Chaos Lab metrics
| Metric | Value |
|---|---|
| Domain Rating | 0 no change since last check |
| Trust Flow | 0 no change since last check |
| Citation Flow | 0 no change since last check |
| Referring domains | 0 no change since last check |
| External backlinks | 0 no change since last check |
Fact: Ahrefs Domain Rating checked 16 Nov 2026, fact changed 13 Nov 2026. Fact: Majestic checked 13 Nov 2026, fact changed 13 Nov 2026. Link facts from Majestic. Trust Flow, Citation Flow and Topical Trust Flow are trademarks of Majestic-12 Ltd.
SAML Chaos Lab domain fact sheet
Open the fact sheet
| Domain age | 5 months |
|---|---|
| Registered | |
| Expires | |
| Registrar | Cloudflare, Inc. |
| DNSSEC | Not signed |
SAML Chaos Lab launch receipt sheet
What we have measured for SAML Chaos Lab since it went live on SaaS Directory Info on 13 November 2026.
- 0 Domain Rating (Ahrefs) no change since launch
at launch: 0 (13 Nov 2026); latest: 15 Nov 2026 - 0 Trust Flow (Majestic)
first measured 13 Nov 2026 - 0 Referring domains (Majestic)
first measured 13 Nov 2026
Day 2 since launch. Next receipt: day 30, 13 Dec 2026. The figures report a change; they do not say what caused it, and many things can. No figure here is a guess.
Got a launch coming up?
Step-by-step tips for before, during and after your launch, free to read on SaaS Directory Info.
- Prepare
- Launch day
- Launch week
- Next steps
Compare and explore
Frequently looked up
- Q1What is the difference between SAML Chaos Lab and standard mock IdP testing?
- Standard staging environments only test happy-path logins with static mock certificates. SAML Chaos Lab acts as an adversarial Identity Provider, injecting dual-key rollovers, XML signature wrapping, expired assertions, and replay attacks directly into the Service Provider before enterprise rollouts to catch real-world failure modes.
- Q2What is the dual-key rollover lockout problem?
- When an enterprise admin schedules a certificate rotation, the IdP publishes a new certificate alongside the existing one. If a Service Provider only binds to a single static certificate in an environment variable, every user is locked out the moment the IdP switches the signing key, causing company-wide SSO outage.
- Q3How does XML signature wrapping attack work?
- Naive XML parsing libraries verify the digital signature against one node in the XML DOM tree but extract user attributes from a different node. SAML Chaos Lab injects all 8 XSW variants to prove the parser is strictly anchored and cannot be exploited to escalate privileges or spoof identity.
- Q4What kind of audit proof does SAML Chaos Lab generate?
- The platform generates machine-readable JSON artifacts signed by the audit engine to satisfy SOC 2 and ISO 27001 cryptographic attestation controls. The signed report includes readiness index, dual-key rollover verification, XSW immunity status, and replay cache configuration.
Leave a review for SAML Chaos Lab
Review count for SAML Chaos Lab: none yet. Add the first.
Fact: reviews are free and cannot be bought. All reviews, in brief
Reviews and facts · Fact updates · Share these facts · Your SaaS? Claim this fact file · Report a wrong fact
SAML Chaos Lab has a free listing. The owner can unlock the full profile with a paid launch for $5:
- Founder story (locked)
- Milestones (locked)
- Demo video (locked)
- Dofollow website link (locked)
See also
| Product | Origin | DR1 | Votes2 |
|---|---|---|---|
 ShipCheckFind security holes in AI-built apps before your users do | New Zealand | 2 | 0 votes. Log in to vote for ShipCheck in the file |
 PassholdA free password manager for Chrome and Edge with autofill, passkeys, password generator, cards and addresses, encrypted on your computer. | not stated | 0 | 0 votes. Log in to vote for Passhold in the file |
 AttraccessMachine access control with qualification checks, machine enablement and session recording | not stated | 15 | 0 votes. Log in to vote for Attraccess in the file |
 NoeticGuardAI DLP for masking PII and secrets before they reach ChatGPT, Claude, Gemini or custom LLM APIs | United States | 5 | 0 votes. Log in to vote for NoeticGuard in the file |