Fact sheet · Cybersecurity
ShipLatch
Security scanning for AI-built apps
Free security scanner that detects leaked keys, exposed files and backend vulnerabilities in apps built with Lovable, Bolt, Replit, Cursor and v0.
Overview
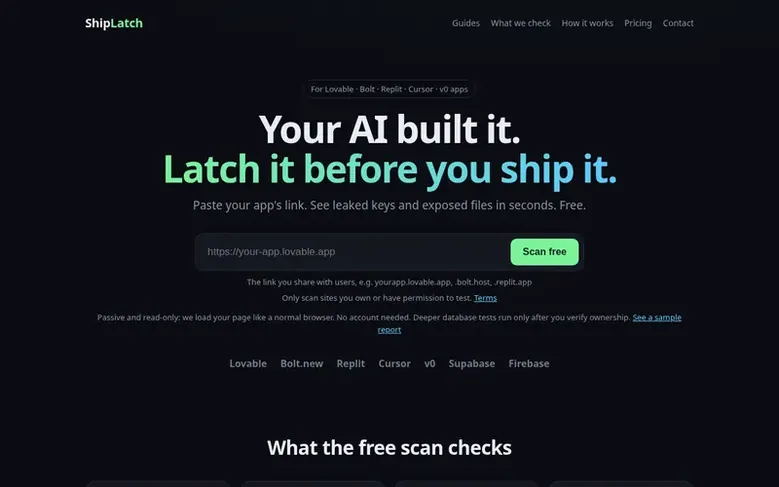
ShipLatch provides automated security scanning for applications built with AI code builders. The free scan checks for leaked API keys (OpenAI, Anthropic, Stripe, AWS, GitHub, Supabase), exposed configuration files like .env and .git folders, backend exposure (Supabase and Firebase detection), and missing security headers. The scan is passive and read-only, loading your public page and up to 20 scripts it references.
Paid plans add copy-paste fix prompts written for your specific AI builder, ownership-verified deep scans that test Row Level Security and Firebase rules, and re-scans to confirm fixes. The Fix Pack ($29 one-time) includes one deep scan and 2 re-scans. Stay Locked ($15/month) adds unlimited re-scans, automatic deployment scanning, and alerts when security grades drop.
Feature facts
- Scans for leaked API keys and secrets from major providers
- Detects exposed .env and .git files
- Checks security headers and missing protections
- Detects Supabase and Firebase backends
- Copy-paste fix prompts for every finding
- Ownership-verified deep scan with RLS testing
- Automatic deployment scanning and grade monitoring
- Passive and read-only scanning
- Scans up to 20 JavaScript bundles and source maps
- Integration with AI assistants via Model Context Protocol
Pricing
Pricing model: Freemium
Free scan: $0. Fix Pack: $29 one-time (includes one deep scan and 2 re-scans for one app, plus 30 days of monitoring). Stay Locked: $15/mo (includes unlimited re-scans of one app, independent scan on every deploy, automatic daily re-scan). DIY playbook: $9 ebook.
Follow ShipLatch: their milestones, new launches and awards come to you by email, once a day by default.
ShipLatch specifications
| Section | Cybersecurity |
|---|---|
| Origin | United States |
| Stage | Startup |
| Website | shiplatch.com |
| Votes2 | 0 |
ShipLatch metrics
| Metric | Value |
|---|---|
| Domain Rating | 0 −1 (down) since last check |
| Trust Flow | 0 no change since last check |
| Citation Flow | 11 no change since last check |
| Referring domains | 1 no change since last check |
| External backlinks | 1 no change since last check |
Fact: Ahrefs Domain Rating checked 12 Nov 2026, fact changed 30 Oct 2026. Fact: Majestic checked 25 Oct 2026, fact changed 25 Oct 2026. Link facts from Majestic. Trust Flow, Citation Flow and Topical Trust Flow are trademarks of Majestic-12 Ltd.
ShipLatch domain fact sheet
Open the fact sheet
| Domain age | 27 days |
|---|---|
| Registered | |
| Expires | |
| Registrar | Cloudflare, Inc. |
| DNSSEC | Not signed |
ShipLatch launch receipt sheet
What we have measured for ShipLatch since it went live on SaaS Directory Info on 25 October 2026.
- 0 Domain Rating (Ahrefs) −1 (down) since launch
at launch: 1 (25 Oct 2026); latest: 11 Nov 2026 - 0 Trust Flow (Majestic)
first measured 25 Oct 2026 - 1 Referring domains (Majestic)
first measured 25 Oct 2026
Day 17 since launch. Next receipt: day 30, 24 Nov 2026. The figures report a change; they do not say what caused it, and many things can. No figure here is a guess.
Got a launch coming up?
Step-by-step tips for before, during and after your launch, free to read on SaaS Directory Info.
- Prepare
- Launch day
- Launch week
- Next steps
Compare and explore
Frequently looked up
- Q1Is my Lovable app secure?
- Security depends mostly on your Supabase setup and Row Level Security configuration. Lovable apps typically ship the Supabase anon key in the browser, which is normal and safe if RLS is enabled on every table with correct policies. Common problems include RLS being turned off, overly permissive policies, service_role keys leaking into frontend code, and secret API keys in client code. ShipLatch's free scan checks the public side for leaked keys, exposed files and headers; the paid deep scan tests your RLS after you verify ownership.
- Q2Is the Supabase anon key safe to expose?
- Yes, the anon (or publishable) key is designed to be public and will always be visible in your frontend. It is only safe if Row Level Security is enabled on every table and your policies are correct, because anyone can use that key to query your database directly. The service_role key is different: it bypasses RLS and must never appear in client code. If it does, rotate it immediately in the Supabase dashboard.
- Q3What does the free ShipLatch scan check?
- The free scan loads your public page and up to 20 scripts it references, plus up to 3 public source maps and one request each to files that should never be public like /.env, /.git/HEAD and supabase/config.toml. It looks for leaked secrets from OpenAI, Anthropic, Stripe, AWS, GitHub, Supabase and more, exposed files, missing security headers, source maps, and whether you use Supabase or Firebase. The scan is passive and read-only with no logins, form submissions, or attack attempts.
- Q4What do the Fix Pack and Stay Locked add?
- Both unlock copy-paste fix prompts for every finding and the ownership-verified deep scan, which includes a read-only Supabase RLS probe that requests zero rows and reads only row counts, plus Firebase security rules checks. The Fix Pack ($29 one-time) includes one deep scan and 2 re-scans for one app. Stay Locked ($15/month) includes unlimited re-scans of one app, an independent scan on every deploy with grade drop alerts, a deploy hook URL for Vercel, Netlify or GitHub Actions, and an automatic daily re-scan.
- Q5How do I check my app for leaked API keys?
- Open your live site, view the page source and the JavaScript bundles it loads (browser dev tools, Sources tab), and search for key prefixes like sk-, sk_live_, AKIA, ghp_, service_role or sb_secret_. Also try opening /.env and /.git/HEAD on your domain. ShipLatch's free scan does exactly this automatically for the page and up to 20 scripts. If you find a secret key, rotate it with the provider; deleting it from the code is not enough once it has been public.
Leave a review for ShipLatch
Review count for ShipLatch: none yet. Add the first.
Fact: reviews are free and cannot be bought. All reviews, in brief
Reviews and facts · Fact updates · Share these facts · Your SaaS? Claim this fact file · Report a wrong fact
ShipLatch has a free listing. The owner can unlock the full profile with a paid launch for $5:
- Founder story (locked)
- Milestones (locked)
- Demo video (locked)
- Dofollow website link (locked)
See also
| Product | Origin | DR1 | Votes2 |
|---|---|---|---|
 T4X ProtectionDefense at the Atom | Bangladesh | 0 | 0 votes. Log in to vote for T4X Protection in the file |
 VeilleStop bots and account abuse in minutes | France | 22 | 0 votes. Log in to vote for Veille in the file |
 KairalBot protection and fraud prevention for e-commerce sites and marketplaces | Italy | 6 | 0 votes. Log in to vote for Kairal in the file |
 falc0nIndependent security researcher mapping India and APAC's exposed attack surface at internet scale | India | 0 | 0 votes. Log in to vote for falc0n in the file |