Fact sheet · Cybersecurity

ZenVeil
Security scanner for AI-generated code that catches secrets, CVEs, and OWASP vulnerabilities in under 30 seconds and auto-fixes with GitHub PRs
DevSecOps scanner that detects secrets, CVEs, and OWASP vulnerabilities in AI-generated code with automated GitHub PR remediation.
Overview
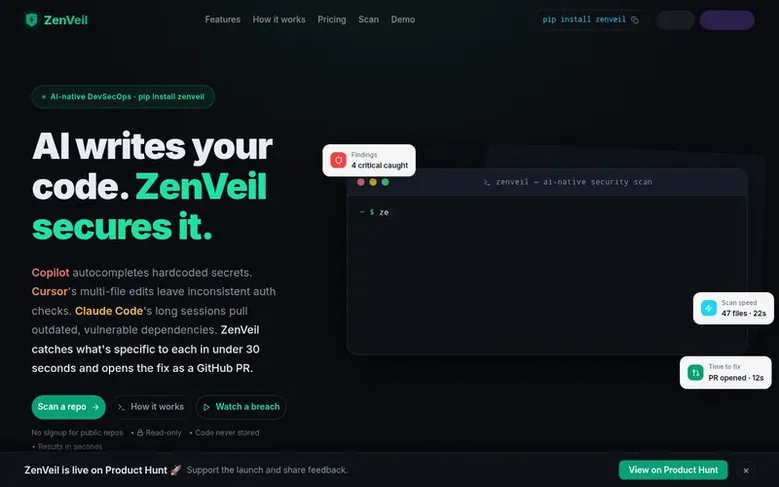
ZenVeil is an AI-native DevSecOps security scanner built for developers using AI coding assistants like Copilot, Cursor, and Claude. It detects three categories of vulnerabilities that AI-generated code introduces at higher frequency: hardcoded secrets and credentials, CVE-vulnerable dependencies, and OWASP Top 10 vulnerabilities. The tool completes full scans in under 30 seconds with read-only access to GitHub repositories, never storing source code. When vulnerabilities are found, ZenVeil automatically opens a GitHub pull request with remediation suggestions powered by AI explanations, enabling fixes without manual triage. The scanner includes 200+ secret detection patterns, CVE lookups via OSV.dev, and specialized rule families tuned to failure modes specific to each major AI coding tool.
Feature facts
- Secret detection with 200+ credential patterns
- CVE vulnerability scanning via OSV.dev
- OWASP Top 10 coverage
- Automated GitHub PR remediation
- AI-powered fix explanations
- Supply chain security analysis
- API security scanning
- CLI and CI/CD integration
- Read-only ephemeral scanning
- Scans complete in under 30 seconds
Pricing
Pricing model: Freemium
Free tier for public repositories with 3 scans per hour; paid plans available for private repositories and higher scan limits
Follow ZenVeil: their milestones, new launches and awards come to you by email, once a day by default.
ZenVeil specifications
| Section | Cybersecurity |
|---|---|
| Website | zenveil.dev |
| Votes2 | 0 |
ZenVeil metrics
| Metric | Value |
|---|---|
| Domain Rating | 0 no change since last check |
| Trust Flow | 1 no change since last check |
| Citation Flow | 13 no change since last check |
| Referring domains | 40 no change since last check |
| External backlinks | 93 no change since last check |
Fact: Ahrefs Domain Rating checked 12 Nov 2026, fact changed 1 Nov 2026. Fact: top topic Computers/News and Media (1). Fact: Majestic checked 1 Nov 2026, fact changed 1 Nov 2026. Link facts from Majestic. Trust Flow, Citation Flow and Topical Trust Flow are trademarks of Majestic-12 Ltd.
ZenVeil domain fact sheet
Open the fact sheet
| Domain age | 5 months |
|---|---|
| Registered | |
| Expires | |
| Registrar | CloudFlare, Inc. |
| DNSSEC | Signed |
ZenVeil launch receipt sheet
What we have measured for ZenVeil since it went live on SaaS Directory Info on 1 November 2026.
- 0 Domain Rating (Ahrefs) no change since launch
at launch: 0 (1 Nov 2026); latest: 12 Nov 2026 - 1 Trust Flow (Majestic)
first measured 1 Nov 2026 - 40 Referring domains (Majestic)
first measured 1 Nov 2026
Day 10 since launch. Next receipt: day 30, 1 Dec 2026. The figures report a change; they do not say what caused it, and many things can. No figure here is a guess.
Got a launch coming up?
Step-by-step tips for before, during and after your launch, free to read on SaaS Directory Info.
- Prepare
- Launch day
- Launch week
- Next steps
Compare and explore
Frequently looked up
- Q1How does ZenVeil keep my code private?
- Repositories are cloned to an ephemeral sandbox with read-only access. Source code is never stored and is deleted after the scan completes. It is never used for training.
- Q2How long does a scan take?
- ZenVeil completes full scans in under 30 seconds, with the ability to scan large repositories including those with approximately 48,000 files in under 8 minutes.
- Q3Does ZenVeil replace my existing security tools?
- No. ZenVeil is designed to complement existing tools like GitHub Actions, Snyk, and Semgrep. It catches specific failure modes from AI-generated code that general-purpose security tools were not designed to detect.
- Q4How many types of vulnerabilities does ZenVeil detect?
- ZenVeil detects three main categories: hardcoded secrets using 200+ patterns, CVE-vulnerable dependencies via OSV.dev, and OWASP Top 10 vulnerabilities including missing auth checks, token storage risks, and more.
- Q5Can ZenVeil integrate with my CI/CD pipeline?
- Yes. ZenVeil can be added to GitHub Actions workflows to automatically scan pull requests, block merges on high-severity findings, and open auto-fix PRs, all in under 30 seconds.
Leave a review for ZenVeil
Review count for ZenVeil: none yet. Add the first.
Fact: reviews are free and cannot be bought. All reviews, in brief
Reviews and facts · Fact updates · Share these facts · Your SaaS? Claim this fact file · Report a wrong fact
ZenVeil has a free listing. The owner can unlock the full profile with a paid launch for $5:
- Founder story (locked)
- Milestones (locked)
- Demo video (locked)
- Dofollow website link (locked)
See also
| Product | Origin | DR1 | Votes2 |
|---|---|---|---|
 T4X ProtectionDefense at the Atom | Bangladesh | 0 | 0 votes. Log in to vote for T4X Protection in the file |
 VeilleStop bots and account abuse in minutes | France | 22 | 0 votes. Log in to vote for Veille in the file |
 KairalBot protection and fraud prevention for e-commerce sites and marketplaces | Italy | 6 | 0 votes. Log in to vote for Kairal in the file |
 falc0nIndependent security researcher mapping India and APAC's exposed attack surface at internet scale | India | 0 | 0 votes. Log in to vote for falc0n in the file |